
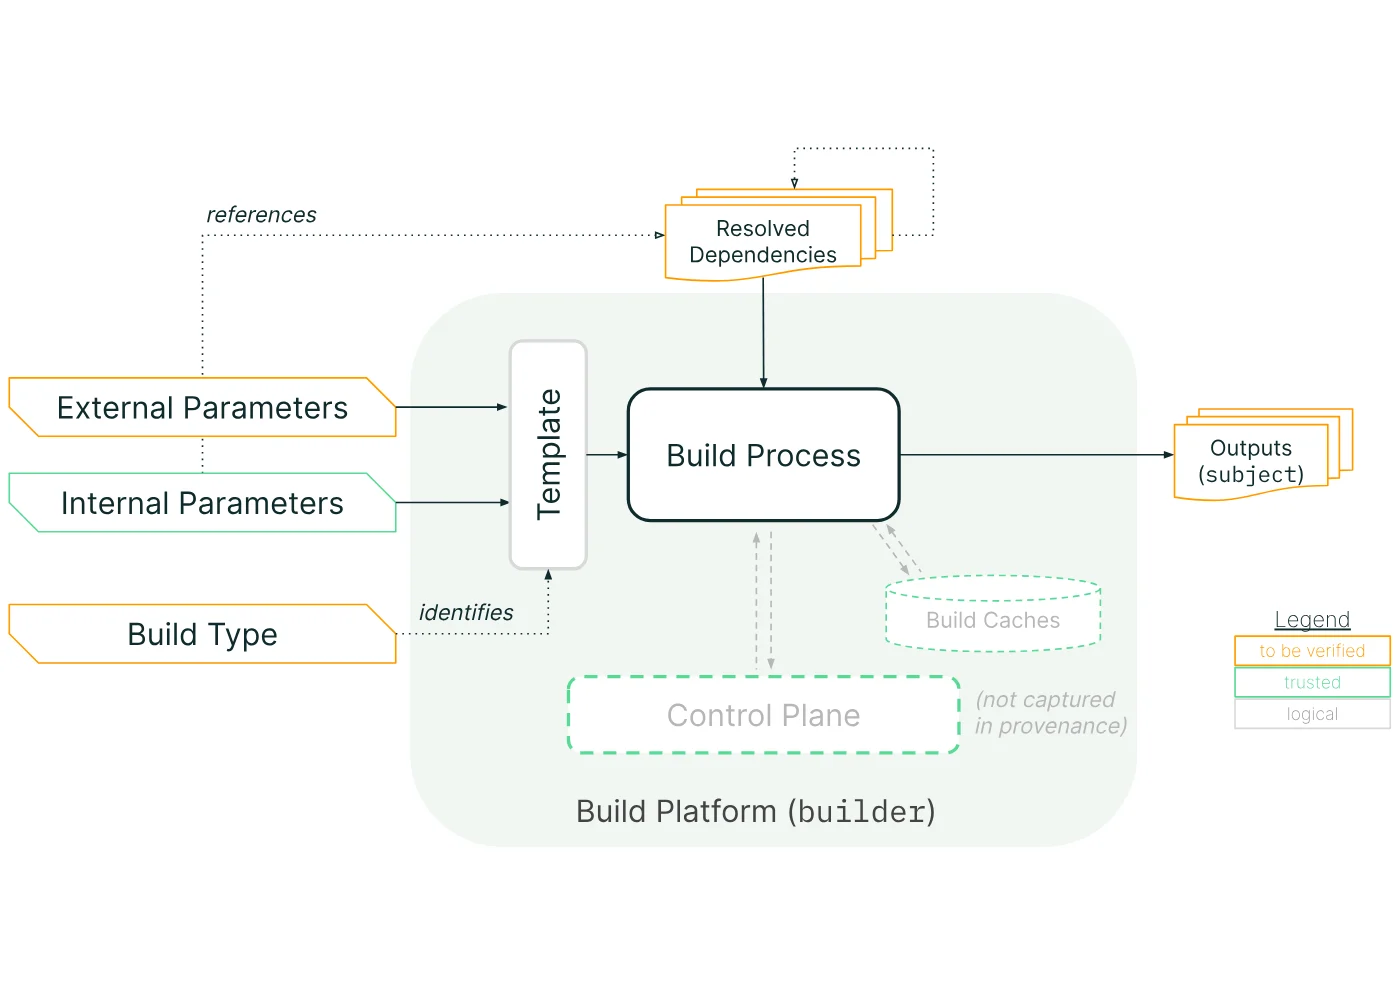
SLSA Build Provenance provides verifiable information about how a software artifact was produced. This guide explains the main provenance fields, the relationship between a subject and its build definition, builder identity, resolved dependencies, run details and the trust assumptions behind verification.
It also covers practical integration into CI/CD pipelines, signature and trust-root management, policy enforcement, common implementation mistakes and a staged adoption checklist. The guide follows the official SLSA v1.2 specification and distinguishes what the standard requires from local engineering choices.
This page provides a concise English summary. The full long-form analysis is currently available in Persian.


