
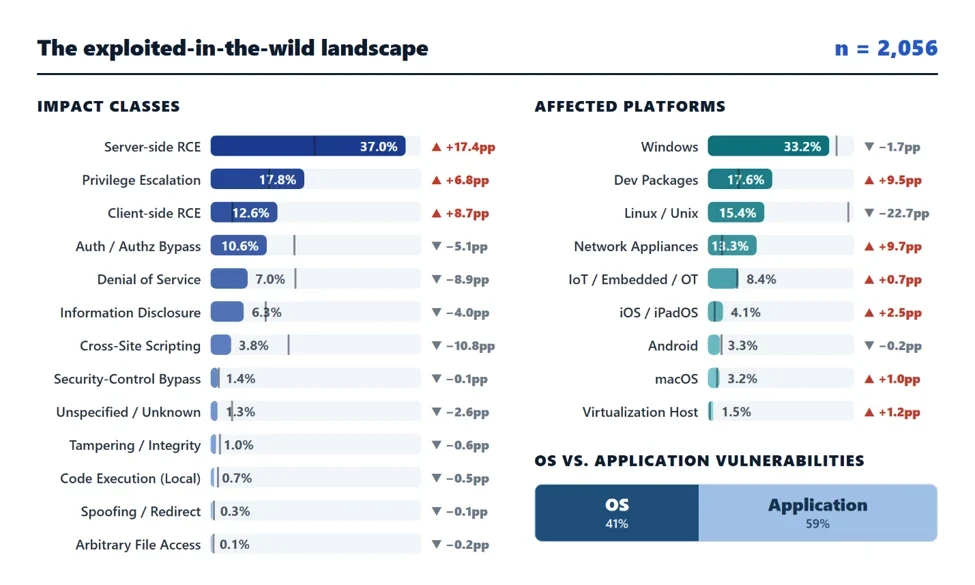
Microsoft Security Research published a data-driven analysis of vulnerabilities observed in real-world attacks. The report emphasizes that defenders should not treat every published CVE as equally urgent: the practical risk depends on exposure, exploitability, the affected system's role and the attack path available to an adversary.
This Persian report examines the findings, explains how vulnerability prioritization can be connected to asset inventory and identity controls, and discusses why patching must be paired with exposure reduction, monitoring and incident readiness. Figures and conclusions are attributed to Microsoft's original research; details not stated by the source are not presented as facts.
This page provides a concise English summary. The full long-form analysis is currently available in Persian.


